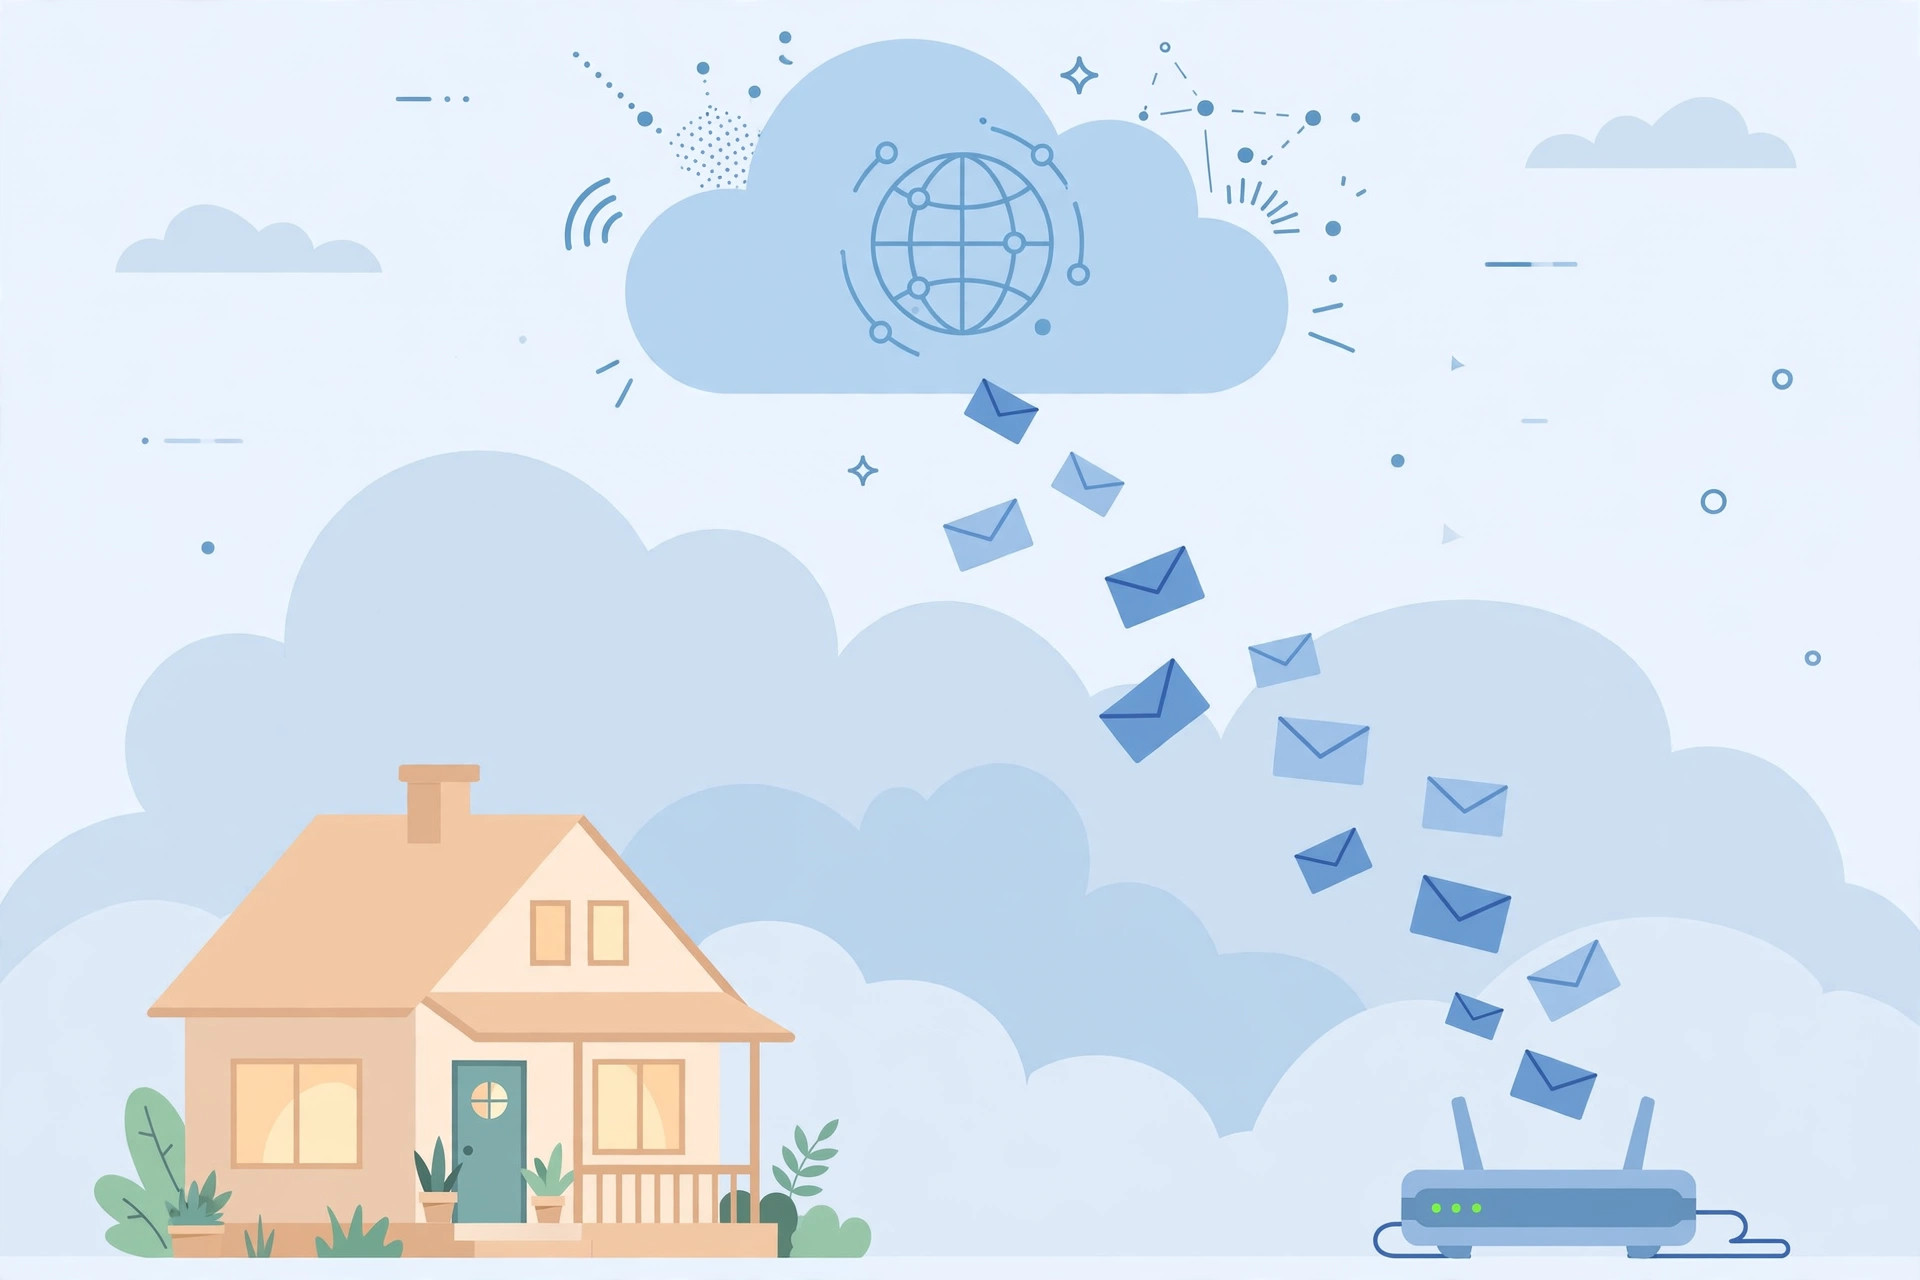
Setting up an smtp relay home server sounds like overkill until your self-hosted apps start failing to send mail. Whether you run Nextcloud, Home Assistant, a personal blog, or a lab full of monitoring scripts, every one of them needs reliable outbound email — and routing it through Gmail or a random SMTP provider eventually becomes a hassle. A home SMTP relay gives you a single, local mail endpoint that everything on your network can use.
In this guide, you will learn the two realistic architectures for a home relay, how to check whether your ISP blocks port 25, and how to configure Postfix as a relay-only smarthost that sends mail securely through an upstream relay.
Why Run a Home SMTP Relay?
A home SMTP relay is not about competing with Gmail. It is infrastructure glue for your homelab. Instead of configuring SMTP credentials separately in every application, you point them all at one internal address — say, 192.168.1.10:587 — and the relay handles the rest. Centralizing outbound mail means:
- One configuration to manage. Change credentials or routing once, not in twelve apps.
- Consistent sender identity. SPF and DKIM only need to cover one relay path.
- Offline queuing. If the internet drops, Postfix queues messages and retries instead of losing them.
- Logging and rate control. You can see exactly what your apps are sending and throttle them per sender.
The Port 25 Problem: Residential ISPs Block It
Before you design anything, face the central constraint of any smtp relay home project: almost all residential ISPs block outbound port 25, and most block inbound port 25 too. This is not malice — it is how ISPs stop infected home routers from becoming spam bots.
Check your own connection with a quick test:
nc -vz smtp.gmail.com 25
telnet gmail-smtp-in.l.google.com 25
If the connection times out (rather than connecting and showing an SMTP banner), your ISP is filtering port 25. There are three workarounds:
- Use submission ports — ports 587 (STARTTLS) and 465 (implicit TLS) are almost never blocked.
- Relay through an upstream smarthost — your home Postfix sends to a VPS or mail provider on port 587, which delivers to the world on your behalf.
- Use DynDNS — if you ever receive mail or run services at home, a dynamic DNS hostname (e.g.,
mail.yourdyndns.net) keeps your server reachable as your IP changes.
In practice, the smarthost approach is the only one that works reliably from a home connection.
Architecture 1: Direct Delivery From Home (Not Recommended)
Direct delivery means your home server connects directly to recipients' mail servers (MX records) on port 25. In theory it is the simplest setup: Postfix with an empty relayhost. In reality it is broken from a residential line:
- Your ISP blocks outbound port 25, so delivery attempts fail outright.
- Residential IP ranges are listed in policy blocklists (PBLs) used by Spamhaus and others — receiving servers reject or spam-folder your mail.
- Dynamic IPs mean no stable reverse DNS (PTR record), and many servers reject mail from hosts without matching forward/reverse DNS.
Direct delivery only becomes viable on a business connection with a static IP, proper PTR records, and port 25 explicitly unblocked. For everyone else, it is a dead end — which is why most guides (including this one) converge on the smarthost model.
Architecture 2: Relay Through a VPS Smarthost (Recommended)
This is the architecture that actually works for a home smtp relay: your home Postfix acts as the local relay for your LAN, then forwards everything to an upstream smarthost on port 587 with authentication. The smarthost — a small VPS with a static IP — does the final delivery to recipients' MX servers on port 25.
The VPS solves all three residential problems at once: port 25 is open from a data center, the IP is static, and you can set a PTR record. A cheap VPS is plenty since it only relays — it does not need storage or CPU. Contabo VPS plans start at very low monthly prices and work well as a dedicated relay box, and RackNerd offers similarly affordable options with unmetered bandwidth. Just make sure your provider allows outbound port 25 — many block it by default and open it on request.
SMTP Relay Home Setup with Postfix
Install Postfix on your home server (Ubuntu/Debian example):
sudo apt update
sudo apt install postfix libsasl2-modules
During installation, choose Internet with smarthost. Then edit /etc/postfix/main.cf with the essentials for a relay-only home setup:
# Basic identity
myhostname = mail.home.lan
mydomain = home.lan
myorigin = $mydomain
mydestination = localhost, $myhostname, localhost.$mydomain
mynetworks = 127.0.0.0/8, 192.168.1.0/24
relayhost = [your-vps.example.com]:587

# Outbound-only: we don't receive mail for real domains
inet_interfaces = localhost, 192.168.1.10

# SASL auth to the upstream smarthost
smtp_sasl_auth_enable = yes
smtp_sasl_password_maps = hash:/etc/postfix/sasl_passwd
smtp_sasl_security_options = noanonymous
smtp_tls_security_level = encrypt
smtp_tls_note_starttls_offer = yes

# Limit the relay to your LAN — no open relay
smtpd_recipient_restrictions = permit_mynetworks, reject_unauth_destination
Storing the Smarthost Credentials
Put the upstream credentials in /etc/postfix/sasl_passwd:
[your-vps.example.com]:587 relayuser:strongpassword
Then hash the file and lock down permissions:
sudo postmap /etc/postfix/sasl_passwd
sudo chmod 600 /etc/postfix/sasl_passwd /etc/postfix/sasl_passwd.db
sudo systemctl reload postfix
Note smtp_tls_security_level = encrypt: this forces TLS to the smarthost, so your credentials and message contents never cross the internet in cleartext.
Authentication: SPF and DKIM
Getting mail delivered is only half the job — it also has to pass authentication checks at the receiving server. Two things matter here:
- SPF: Your domain's SPF record must authorize the server that actually connects to recipients' MX hosts — that is the smarthost VPS, not your home IP. A typical record looks like
v=spf1 ip4:203.0.113.25 include:_spf.google.com ~all, where theip4entry is your VPS address. Never put a dynamic home IP in SPF. - DKIM: Sign messages before they leave. The cleanest approach is to run DKIM signing on the smarthost VPS itself (with OpenDKIM or Rspamd), since that is the machine with a stable identity and PTR record. Your home relay then stays simple and stateless.
DMARC follows naturally once SPF and DKIM both align on your sending domain. Start with p=none and read the reports before tightening to quarantine or reject.
Testing Your Home Relay
Install swaks (the Swiss Army Knife for SMTP) on any LAN machine and send a test through your relay:
swaks --to [email protected] \
  --from [email protected] \
  --server 192.168.1.10:587 \
  --header "Subject: Home relay test"
Then watch the mail log on the relay host:
sudo tail -f /var/log/mail.log
A healthy relay shows status=sent entries flowing through the smarthost. Common failures: SASL authentication failed (wrong credentials in sasl_passwd — check for typos and rerun postmap), or must issue a STARTTLS command first (the smarthost requires TLS; verify smtp_tls_security_level).
Security: Never Run an Open Relay
An open relay — a server anyone on the internet can send mail through — will be found by spammers within hours and will get your VPS IP blacklisted. Your setup is protected by two rules:
mynetworksonly includes localhost and your LAN subnet, andsmtpd_recipient_restrictionsrejects unauthenticated relay attempts from everywhere else.- If you ever expose port 587 on the relay itself (for sending mail while traveling), require SASL authentication with strong passwords on that listener.
Keep Postfix updated, and consider rate-limiting per-sender with postfwd or Postfix's built-in smtpd_client_message_rate_limit if a chatty app starts flooding the queue.
Alternatives: Managed SMTP Relay Services
If running even a small VPS smarthost feels like too much maintenance, managed relay services (SMTP2GO, SendGrid, Mailgun, Amazon SES) offer the same port-587-with-auth model without any server to patch. You point your home Postfix relayhost at their endpoint instead of your own VPS. The tradeoff is cost at scale and less control over IP reputation — but for a homelab sending a few hundred notifications a day, the free tiers are usually generous.
Frequently Asked Questions
Can I receive mail at home too?
Technically yes, but inbound delivery needs inbound port 25 (usually blocked), MX records pointing at a DynDNS hostname, and constant uptime. Most home operators receive mail at their VPS or provider mailbox instead.
Will my mail land in spam?
It should not, as long as the smarthost has a clean static IP, a matching PTR record, valid SPF, and DKIM signatures. Warm up gradually — sudden bursts of mail from a fresh IP raise flags.
How do I handle a changing home IP?
The home relay only talks to your smarthost on port 587 with SASL auth, so a changing home IP affects nothing. If you allow-list the home IP on the VPS firewall, use a DynDNS hostname in the allow rule instead of a static IP.
Key Takeaways
- A home SMTP relay centralizes outbound mail for all your self-hosted apps behind one local endpoint.
- Residential ISPs block port 25 and residential IPs sit on policy blocklists, so direct delivery from home rarely works.
- The proven design is a home Postfix relay forwarding to a VPS smarthost over port 587 with SASL auth and enforced TLS.
- SPF must authorize the smarthost VPS (static IP), and DKIM signing belongs on the smarthost, not the home server.
- Restrict the relay to your LAN — never expose an unauthenticated relay to the internet.
- Managed relay services are a valid low-maintenance alternative if you skip the VPS.