

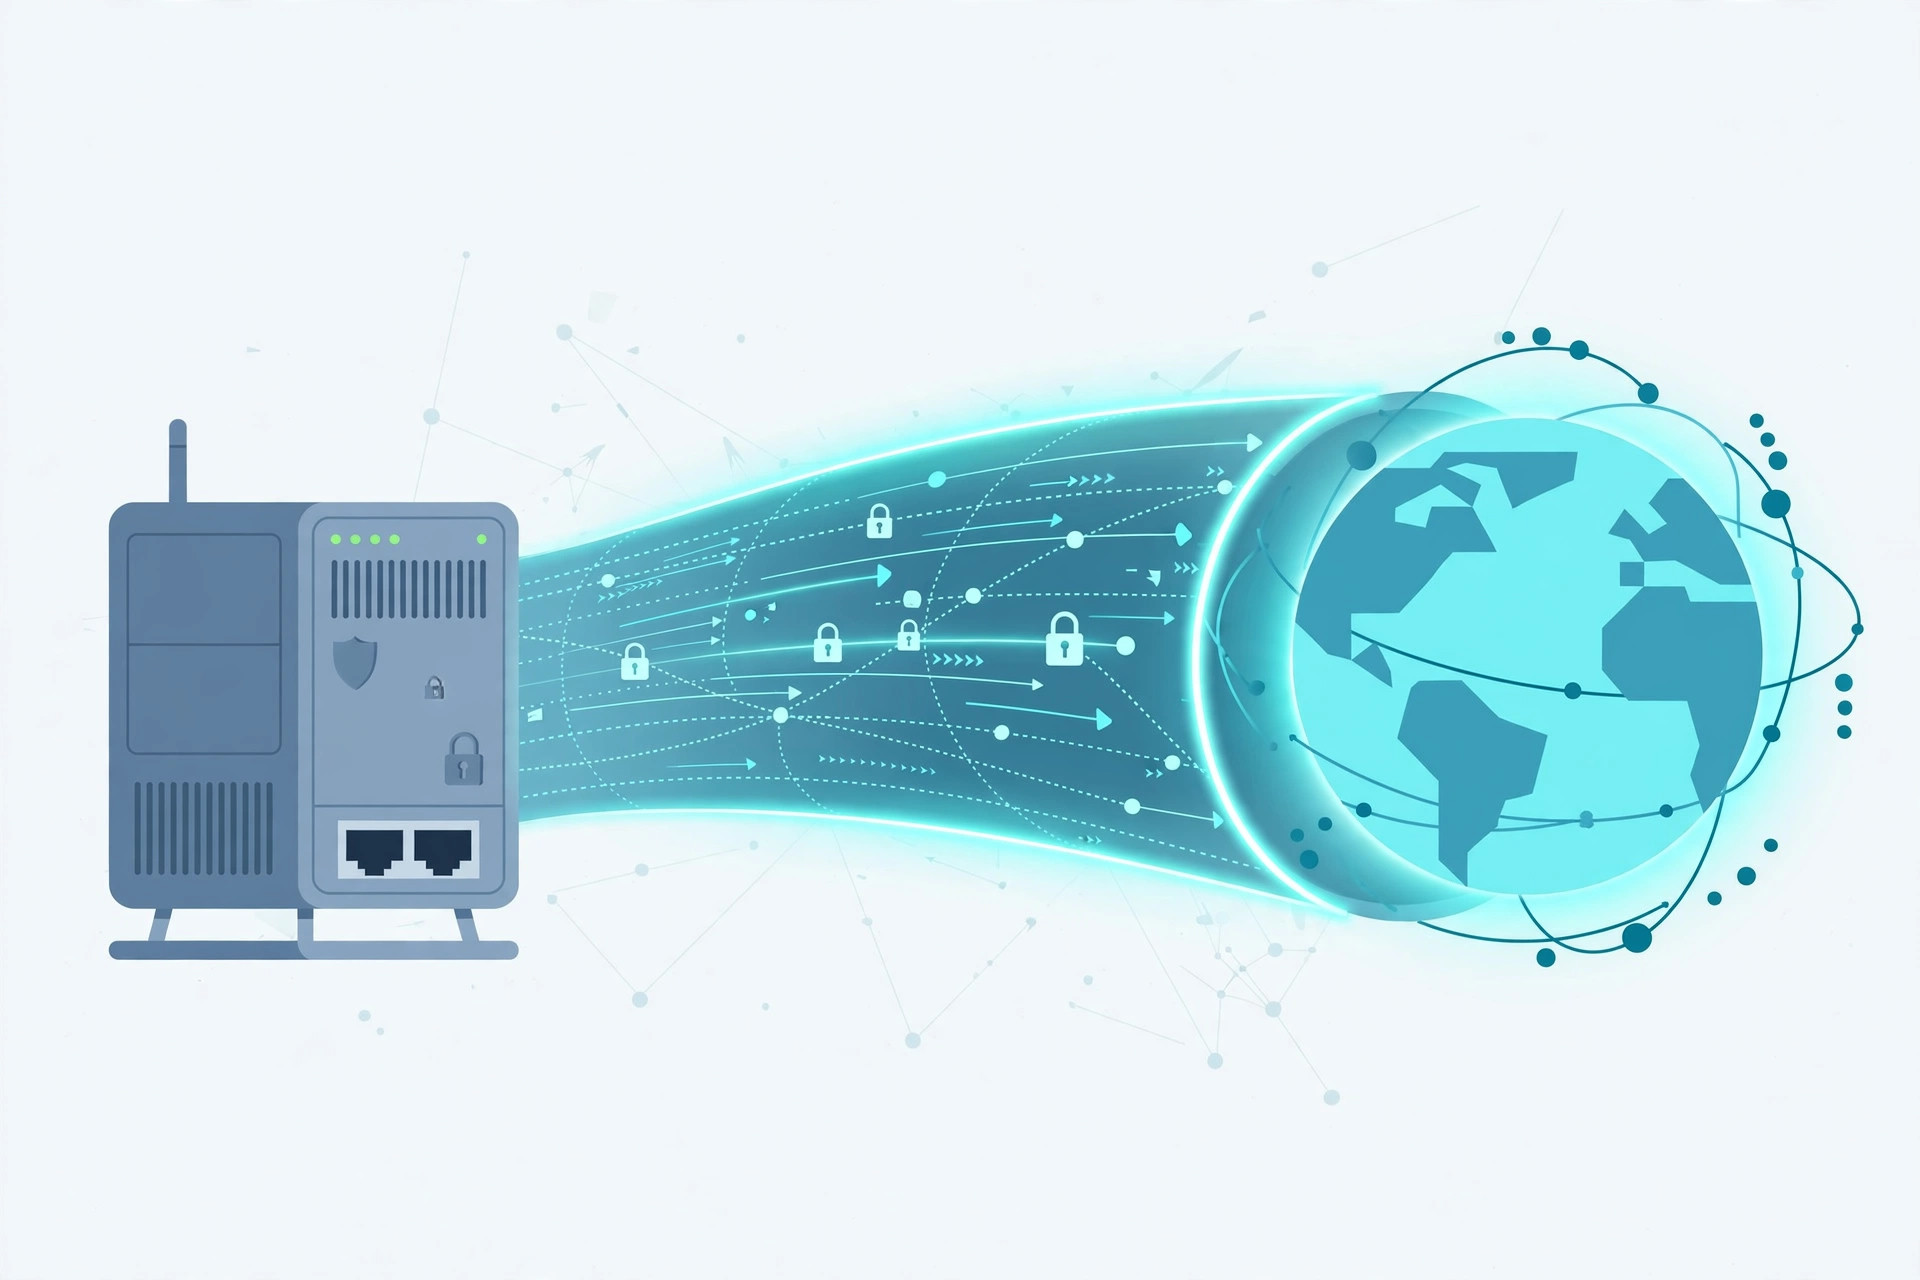
Exposing a self-hosted app to the internet usually means port forwarding, dynamic DNS, and hoping your ISP does not block inbound ports. A Cloudflare Tunnel does it better: it creates a secure outbound connection from your server to Cloudflare's network, so your apps become reachable on a public domain without opening a single inbound port on your firewall or router. This guide explains what a Cloudflare Tunnel is, when to use one, and exactly how to set it up on Linux in 2026.
What Is a Cloudflare Tunnel?
A Cloudflare Tunnel (built on the cloudflared daemon) is an encrypted tunnel between your server and Cloudflare's edge network. Instead of the internet connecting directly to your machine, all traffic flows through Cloudflare: visitors hit your domain, Cloudflare proxies the request down the tunnel, and your app responds back through the same secure channel. Your server's real IP address is never exposed, and you never need to open ports 80 or 443 inbound.
The free Cloudflare plan includes tunnels at no cost, which makes this one of the cheapest ways to publish home-lab dashboards, development servers, webhooks, and small production apps securely. It also works behind CGNAT and on networks where you have zero control over the router, since the connection is initiated outbound from your server.
Cloudflare Tunnel vs Port Forwarding
Traditional port forwarding punches holes in your firewall and exposes your public IP to every scanner on the internet. A Cloudflare Tunnel flips the model: only outbound HTTPS connections leave your network, so there is nothing listening for attackers to find. You also get Cloudflare's DDoS protection, Web Application Firewall rules, and CDN caching in front of your app for free.
The trade-offs are real, though. All traffic routes through Cloudflare, which adds a small amount of latency and means Cloudflare can technically see your traffic (use end-to-end TLS with a valid certificate on your origin if that matters). Very high-bandwidth uses like game servers or large file transfers are better served by a direct connection or a VPS with a public IP. For dashboards, APIs, blogs, and internal tools, a Cloudflare Tunnel is almost always the simpler and safer choice.
How to Set Up a Cloudflare Tunnel on Linux
Follow these steps to create your first Cloudflare Tunnel. You need a domain already added to Cloudflare (free plan is fine) and a Linux server or PC with the app running on localhost.
Step 1: Install cloudflared
On Debian or Ubuntu, install the official package:
curl -fsSL https://pkg.cloudflare.com/cloudflare-main.gpg | sudo tee /usr/share/keyrings/cloudflare-main.gpg >/dev/null
echo 'deb [signed-by=/usr/share/keyrings/cloudflare-main.gpg] https://pkg.cloudflare.com/cloudflared any main' | sudo tee /etc/apt/sources.list.d/cloudflared.list
sudo apt update && sudo apt install -y cloudflared
Verify the install with cloudflared --version.
Step 2: Authenticate with Your Cloudflare Account
Run the login command and open the printed URL in your browser to authorize the tunnel:
cloudflared tunnel login
This downloads a certificate to ~/.cloudflared/cert.pem that lets cloudflared manage tunnels and DNS records in your account.
Step 3: Create the Tunnel
Create a named tunnel (use a descriptive name like homelab):
cloudflared tunnel create homelab
Note the tunnel ID from the output. Then create a configuration file at ~/.cloudflared/config.yml:
tunnel: YOUR-TUNNEL-ID
credentials-file: /home/USERNAME/.cloudflared/YOUR-TUNNEL-ID.json

ingress:
  - hostname: app.yourdomain.com
    service: http://localhost:3000
  - service: http_status:404
Replace the hostname with your domain and the service URL with whatever your app listens on.
Step 4: Route DNS and Start the Tunnel
Create the DNS record that points your hostname at the tunnel:
cloudflared tunnel route dns homelab app.yourdomain.com
Then run the tunnel in the foreground to test it:
cloudflared tunnel run homelab
Visit https://app.yourdomain.com. If your app loads with a valid Cloudflare certificate, the Cloudflare Tunnel is working.
Step 5: Run the Cloudflare Tunnel as a Service
For production use, install it as a systemd service so it starts on boot and restarts on failure:
sudo cloudflared service install
sudo systemctl enable --now cloudflared
Check status anytime with sudo systemctl status cloudflared. You can also manage the tunnel from the Cloudflare dashboard under Zero Trust > Networks > Tunnels, where you can edit ingress rules without touching the config file.
Securing Your Cloudflare Tunnel
A tunnel hides your IP, but you should still lock the app itself down:
- Add Cloudflare Access: put an identity check (Google login, one-time PIN) in front of private dashboards so only you can open them.
- Enable bot protection: turn on “Under Attack Mode” or bot fight mode for public-facing apps during incidents.
- Use authenticated origin pulls: configure your origin web server to only accept connections presenting Cloudflare's client certificate.
- Keep cloudflared updated: the daemon auto-updates when run as a service on most distros; verify with
cloudflared --versionoccasionally.
Common Cloudflare Tunnel Use Cases
Beyond the obvious home-lab dashboards (Plex, Nextcloud, Home Assistant), a Cloudflare Tunnel is perfect for receiving webhooks during local development, sharing a staging site with a client, running a personal blog from a Raspberry Pi, or giving a VPS-hosted app DDoS protection without paying for it. If you later outgrow the tunnel model, moving the same app to a public VPS is easy; providers like Ultahost or Contabo give you a cheap public server, and our VPS provider guide helps you choose.
Key Takeaways
- A Cloudflare Tunnel exposes local apps on a public domain without opening any inbound firewall ports.
- It is free on Cloudflare's free plan and works behind CGNAT, dynamic IPs, and locked-down routers.
- Setup takes five steps: install cloudflared, log in, create the tunnel, route DNS, and run it as a service.
- Your origin IP stays hidden and you get Cloudflare's DDoS protection and WAF in front of every tunneled app.
- Add Cloudflare Access in front of private dashboards for an extra identity-based security layer.
Related Guides
- Best VPS Providers with Open Port 25 — when you are ready to move from a tunnel to a public server.
- How to Install Zimbra Mail Server — another self-hosted service you can protect behind a tunnel.